Data Protection & Compliance

A Data Protection Officer and Grievance Officer, Without a Full-Time Hire

Brain Cyber Solutions offers Data Protection Officer (DPO) and Grievance Officer support as a yearly service, in partnership with Vectis Trust. Only organisations notified as Significant Data Fiduciaries must appoint a statutory DPO; other businesses still need a published contact and a grievance process. You get a clear privacy contact, a working route for grievances and rights requests, and records of what was done, without hiring a full-time officer. Privacy contact and grievance management starts from Rs. 35,000 + GST a year; a formal DPO appointment is quoted separately.

What you receive

  • A published privacy and grievance contact route
  • Grievance intake, tracking and closure records
  • Coordination of access, correction and deletion requests
  • Consent and withdrawal follow-up with your teams
  • Incident escalation and notification preparation support

and 2 more

  • PricingPrivacy contact and grievance: from Rs. 35,000 + GST a year
  • CoversDPO and Grievance Officer roles
  • Main duties start13 May 2027
  • PartnerVectis Trust

The problems we solve

Does this sound familiar?

These are the everyday challenges we help businesses solve.

  1. Nobody owns data protection

    It is a side job for someone in IT, HR or admin, so it waits until there is a complaint.

  2. There is no route for complaints

    A customer who wants their data removed does not know who to ask, and your team does not know how to respond.

  3. Requests get lost

    Access, correction and deletion requests arrive by WhatsApp or email, with no owner and no record.

  4. A full-time officer is hard to justify

    A small or mid-sized business rarely has enough privacy work for a dedicated salary.

Who this is for

Small and mid-sized businesses that need a clear privacy contact and a working grievance process, and organisations that may be notified as Significant Data Fiduciaries and want to prepare. It suits clinics, schools and institutes, retailers, IT companies and any business without a privacy specialist on staff.

DPO or Grievance Officer: which do you need?

Only organisations notified as Significant Data Fiduciaries must appoint a statutory Data Protection Officer. Most businesses are not in that group, but they still need a published contact for data questions and a way to handle grievances. For them, "DPO as a service" is the name of the support, not a statutory appointment. We will tell you plainly which applies to you.

Two levels of support

  • Privacy contact and grievance management, from Rs. 35,000 + GST a year:for businesses that need someone to handle privacy enquiries, rights requests, grievances and records.
  • Fractional Data Protection Officer, quoted separately:for organisations that must appoint a DPO, or choose to, subject to a review of the requirements, independence and reporting for that engagement.

Your written proposal confirms which level you are getting, the expected volume, response times and what is excluded, including legal services.

What stays with you

Your organisation remains accountable. The service provides the contact, coordination and records. Your team supplies the information and decisions, and carries out changes in your systems. If you want help with those changes, see technical implementation.

Where this fits

Most businesses start with an initial assessment and implementation support, then keep this service running through the year. See all our DPDP compliance services.

This page is general information, not legal advice.

Pricing

Privacy contact and grievance management from Rs. 35,000 + GST a year.

A formal Data Protection Officer appointment is quoted separately. Both depend on your size, how many requests you receive and how much oversight you need. Your written proposal gives one final price that includes everything agreed.

How the work runs

How the service runs.

Set up the function first, then keep it working through the year.

  1. Scope

    We review your data, regulatory status and request volumes, and agree the role and contact.

  2. Set up

    We set up the contact route, registers, reporting lines and a first action plan.

  3. Operate

    Grievances and requests are received, tracked, coordinated with your team and closed with records.

  4. Report

    You receive regular reports, and anything serious is escalated to your management.

Included

What you receive

Your written proposal confirms exactly what is included for your scope.

  1. A published privacy and grievance contact route

  2. Grievance intake, tracking and closure records

  3. Coordination of access, correction and deletion requests

  4. Consent and withdrawal follow-up with your teams

  5. Incident escalation and notification preparation support

  6. A compliance calendar and open-action register

  7. Regular reports for your management

Questions

Questions about DPO and Grievance Officer services

Does every business need a Data Protection Officer?

No. The DPDP Act requires a Data Protection Officer based in India for organisations notified as Significant Data Fiduciaries. Other organisations do not have to appoint a statutory DPO, but they must publish contact details for someone who can answer questions about personal data.

Do we need a grievance process?

Yes. Under the DPDP Rules, every Data Fiduciary needs a published way for people to raise grievances and must respond within a reasonable period, not exceeding 90 days. These duties apply from 13 May 2027.

What is a Grievance Officer as a service?

An outside team acts as your route for data protection grievances: receiving them, coordinating with your staff, preparing responses and keeping records of what was closed and how.

How much does it cost?

Privacy contact and grievance management starts from Rs. 35,000 + GST a year. A formal DPO appointment is quoted separately. Your written proposal gives one final price that includes everything agreed.

Can a fractional DPO be our formal DPO if we are a Significant Data Fiduciary?

Vectis Trust offers a named India-based individual for appointment, subject to a review of the requirements for that engagement. The appointment duty stays with your organisation, and the role reports to your Board or equivalent governing body.

Does this make us compliant?

No service can promise that. Your organisation stays accountable as the Data Fiduciary and must provide the authority, resources and decisions the role needs. This page is general information, not legal advice.

Who handles the technical side of a breach?

The service coordinates the privacy response: facts, assessment, escalation and preparing notifications. Containment and forensics stay with your technical team or provider.

Talk to the people who do this work

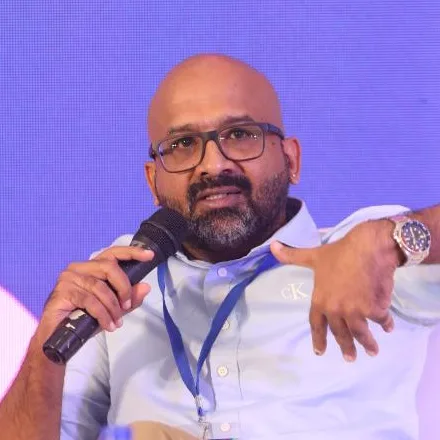
Jayapradeep Jiothis

Jayapradeep Jiothis

Co-Founder & Senior Managing Partner, Vectis Trust

Certified Data Protection Professional · ISO/IEC 42001 Auditor

  • Data Privacy
  • Breach Management
  • Responsible AI

Next step

Know who answers when someone asks about their data.

Message us on WhatsApp with your business type and roughly how much personal data you handle. We reply with what fits and a starting quote.

  • Message or call
  • English or Malayalam
  • Clear next steps